I was offered my first outside job after the second year of highschool, I kinda accidentally interviewed for a at the time respected gamedev firm (since I was looking for a summerjob heh) and when we started talking about when to start and I mentioned my school semesters the interviewer realized that I was younger than he had assumed.
I think it turned out to be mostly one guy, but he wasn't a teenager, anymore, when they finally got him[0]. I know that after that arrest, the group disappeared.
I think that some of the kids they are nailing for ShinyHunters actually ordered hits.
Maybe publicly going after the FBI wasn't such a bright move... They could have kept it quiet, and made millions, selling to bad guys.
[0] https://www.csoonline.com/article/510783/data-protection-flu...
They're trolling him saying he's not nearly as good and tarnishing the ShinyHunters rep.
I have no idea what's true, but they can all go to hell.
Outside of a few cases, it's always been a box checking exercise. If you're fortunate, the boxes are kept up to date / written by somebody that knows what they're doing. If you're like most, the box hasn't changed since the 90s when "complex passwords, changed quarterly" was in vogue.
They need a head on a pike to save face for the FBI, both in front of the public and for internal credibility in government, law enforcement, and within their own origanization. Imagine how the FBI would look if they couldn't find or apprehend the perpetrators. And the current FBI - the leadership and their superiors, at least - seems much more focused on politics than predecessors.
https://krebsonsecurity.com/wp-content/uploads/2025/11/slsh-...
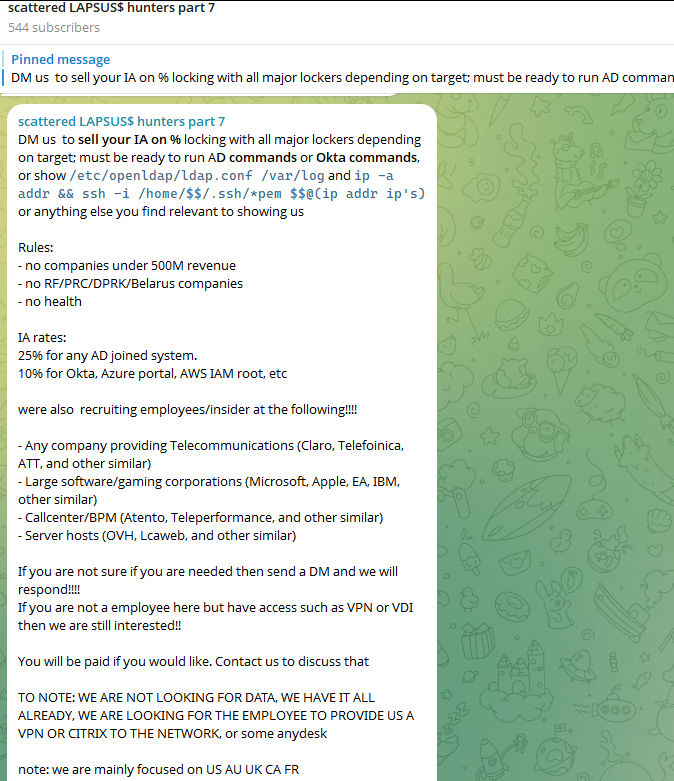
(from https://krebsonsecurity.com/2025/11/meet-rey-the-admin-of-sc... linked in the original post)
It could be practical.
Van der Stap “was sentenced to four years in prison (one suspended) and a three-year probationary period” in 2023, released from prison “in the beginning of 2026,” and then promptly charged “with attempted incitement of two murders” which will presumably put him in jail for a couple more years [1].
China wouldn’t be so lenient.
Last time I tried my hand at whitehat hacking on HackerOne, it took me 30 minutes to find a major system crash/DoS vulnerability in a major platform. The company acknowledged that the issue was real but denied me the bounty payment because they said I would have to 'prove' that it leads to catastrophic failure. I had already done so in the sense that you could reliably infer it from the data I had provided, but it seemed like they were baiting me into committing a felony (DoS attack) to prove my point, which I wasn't prepared to do but I'm sure I could have done cheaply. So yeah, whitehat hacking seems to be a waste of time. Most software today is incredibly insecure.